What Happened
Many beginners know that multi-factor authentication, or MFA, is important, but still treat it as a button to switch on once and forget. The real skill is learning how an account sign-in is protected, choosing a second factor that fits the situation, and preparing a recovery plan before a phone is lost or replaced. This guide explains the basic MFA choices in plain language and gives you a small practice routine you can use to make one important account safer this week.
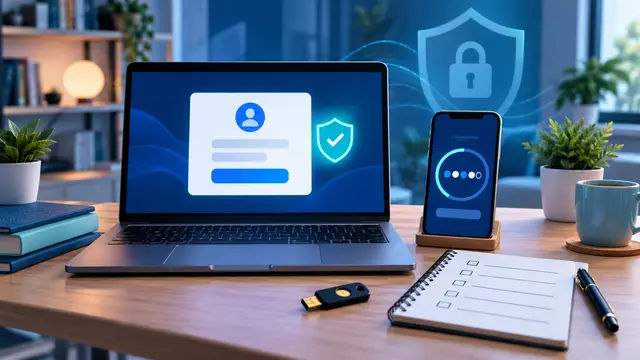
MFA adds another proof of identity after a password. A password proves that someone knows a secret. A second factor asks for something else, such as a code from an authenticator app, a physical security key, or a confirmation on a trusted device. The point is not to make signing in annoying. The point is to make a stolen or guessed password less useful to an attacker.
That distinction matters because passwords are often reused, exposed in old data breaches, or entered into convincing fake sign-in pages. Even a careful person can make a mistake when tired, rushed, or responding to an urgent message. MFA gives an account another checkpoint, so one mistake does not automatically become full access.
Learning MFA is a practical cybersecurity fundamentals exercise because it combines account habits, device awareness, recovery planning, and careful decision-making. You do not need to understand advanced encryption to begin. You need to know what each sign-in prompt means and what you should do when the prompt is unexpected.
Start by separating three ideas that are often mixed together:
- Authentication is the process of proving who you are.
- Authorization is the permission you receive after signing in.
- Recovery is how you regain access when your normal sign-in method is unavailable.
MFA improves authentication. It does not automatically fix excessive permissions, an infected device, or a deceptive website. That is why a good beginner lesson treats MFA as one layer in a larger account-safety routine.
An everyday example makes the concept easier to remember. Imagine a locked office with two doors. The first door opens with a key. The second door opens only after a receptionist checks an employee badge. If someone copies the key, the copied key alone is not enough. MFA works in a similar way, although the factors are digital rather than physical.
The most useful beginner outcome is not memorizing security vocabulary. It is being able to look at a sign-in request and ask, “Did I start this, and do I understand what I am approving?” That question prevents a common mistake: approving an unexpected prompt simply because it looks familiar.
Why It Matters for Businesses
Businesses depend on accounts that hold customer records, payment details, employee information, project files, and internal conversations. A single compromised mailbox can expose password resets, invoices, shared documents, and messages that help an attacker impersonate a trusted employee. For a small company, one account problem can interrupt work for an entire afternoon or create a much longer cleanup.
MFA is especially valuable for ordinary work accounts because those accounts are attractive targets even when the employee is not an administrator. An attacker may use a regular mailbox to request a payment change, collect customer information, or send believable messages to coworkers. Protecting the first account in the chain can stop a larger incident from developing.
The business benefit is easier to see when teams connect the skill to real tasks. A new employee might be setting up a project-management account. A bookkeeper might be signing into an invoicing platform. A small-business owner might be reviewing a shared cloud drive from a hotel. In each case, the person needs to recognize the normal MFA flow and the warning signs of an abnormal one.
Useful workplace habits include:
- Enabling MFA on email, financial, file-sharing, and administrator accounts first.
- Keeping a separate recovery method instead of relying on one phone.
- Reporting repeated unexpected prompts instead of approving them to make the alerts stop.
- Checking the address bar and sign-in page before entering a password or code.
- Reviewing active sessions and removing devices that are no longer trusted.
These habits also reduce confusion for managers. When employees understand the difference between a normal approval and a suspicious request, they can report useful details: the time, device, application, and action they saw. That information helps a business respond quickly without turning every alert into a mystery.
MFA training supports a healthier security culture because it gives people a concrete action they can practice. “Be careful online” is too vague to guide a busy employee. “Pause when a login prompt appears that you did not start, then report it” is specific enough to remember.
There are limits. SMS codes can be easier to intercept than codes created by an authenticator app, and a phone itself can be lost or compromised. A security key can offer strong protection but may require extra planning and a backup key. The right choice depends on the account, the people using it, and the recovery options the service provides.
The beginner lesson is to improve the strongest practical option available rather than waiting for a perfect setup. If an account offers an authenticator app, learn how to use it. If a business requires a security key, practice the sign-in and backup process. If SMS is the only option, enable it while understanding that it is one layer, not a complete security plan.
The Practical Automation Opportunity
MFA becomes easier to learn when it is taught through a small repeatable workflow instead of a long list of warnings. A self-paced course can turn one account setup into a practice project with four stages: identify the account, choose the factor, test recovery, and record the result without storing secrets in an unsafe place.
Here is a beginner-friendly practice exercise. Choose a noncritical personal account or a test workspace where changing sign-in settings will not interrupt anyone else. Do not use an account you cannot afford to lock yourself out of while you are learning.
- Write down why the account matters and what information it protects.
- Review the available MFA choices without enabling anything yet.
- Choose the factor you can use reliably on your normal devices.
- Enable the factor and complete one normal sign-in.
- Test the documented recovery method and confirm that it works.
- Record the account name, setup date, and recovery location without recording the actual one-time codes or password.
The exercise teaches more than clicking Enable. It shows where friction appears. Perhaps the authenticator app is on an old phone. Perhaps the backup codes were downloaded but not stored where the owner can find them. Perhaps the account has an old trusted device that should be removed. Each discovery is part of the learning outcome.
You can also use a simple decision table while comparing factors:
- Authenticator app: convenient for many users and stronger than password-only access, but it depends on a working device and a recovery plan.
- Security key: strong against many fake sign-in attacks, but it requires possession of the key and a backup plan.
- Device approval: quick when the device is trusted, but an unexpected approval should never be accepted automatically.
- SMS code: widely available and easy to understand, but it may provide less protection than other options.
No-code automation can support the learning process without handling private sign-in codes. For example, a team could use a task board to track which departments have completed MFA training. A form could collect the account category, factor type, and completion date. A reminder could notify an employee to review recovery methods every six months. The automation should track readiness, not passwords, secret codes, or screenshots of sensitive prompts.
This is an important boundary for beginners. Automation is useful for reminding people to review a control. It is not a reason to copy authentication codes into a spreadsheet or forward security alerts to a shared inbox. Good workflow design reduces manual follow-up while keeping secrets in the system designed to protect them.
A short course can build confidence through practice scenarios:
- You receive an MFA prompt while your phone is in your hand, but you did not attempt to sign in.
- You replace your phone and realize your authenticator was not transferred.
- A coworker asks you to send a login code so they can “finish setup.”
- You sign in from a new location and the service asks you to confirm the device.
- You discover an old laptop is still listed as an active session.
For each scenario, the learner can identify the safe next action, the information to report, and the recovery setting to review. This is the kind of small, applied practice that makes cybersecurity less abstract. It also works well for busy professionals who want a skill they can use immediately rather than a long theory-first program.
The same approach can extend to a team. Start with one high-value account category, define what “MFA complete” means, and create a short checklist. After the first round, ask which step caused confusion. Improve the instructions based on that feedback. A workflow that employees can complete correctly is more valuable than a complicated policy nobody remembers.
Business Takeaway
MFA is a practical first cybersecurity skill because it connects a simple setting to a real reduction in account risk. The strongest habit is not blindly accepting every prompt. It is understanding the sign-in request, using a factor that fits the account, and preparing recovery before an emergency.
For a business, the learning path can stay small and measurable. Teach employees how to identify an unexpected approval, protect a priority account, review trusted devices, and report a suspicious request. For an individual learner, one carefully chosen practice account is enough to understand the whole cycle from setup to recovery.
This week, choose one important account, compare its available MFA methods, enable the safest practical option, and test the recovery process before you need it.