What Happened
Vendor master data changes look routine until one bad update redirects money, breaks tax reporting, or slows a supplier that the business depends on. A bank account change, remittance email update, tax ID correction, or address edit can move through an ERP queue like simple clerical work, even though it carries real payment and compliance risk. This article explains how AI and automation can help finance and procurement teams review vendor record changes before the update becomes a costly exception.
The problem is not that AP teams ignore controls. The problem is that the change requests arrive in too many forms. One supplier emails a new ACH form to an AP clerk. Another updates a portal profile. A buyer forwards a message from a sales rep at the vendor. A controller receives a bank letter during month-end close and asks someone to handle it quickly. By the time the request reaches the ERP, the reviewer may see only a short note and an attachment, not the full context behind the change.
That is where mistakes become expensive. If the wrong bank account is approved, the company may send a real payment to a fraudulent destination. If a legal name change is entered without matching tax documentation, 1099 reporting may be wrong later. If a vendor address is changed without checking open purchase orders, shipments, returns, or remittance instructions may go sideways. The data field looks small, but the operational consequences are not.
Many companies rely on manual judgment for these updates. An AP specialist checks the document, compares it to the vendor record, asks the buyer if the request seems legitimate, and routes the change to a supervisor when something feels off. That can work when volume is low and the same experienced person handles the queue every day. It becomes weaker when the business adds vendors, expands locations, changes ERP systems, outsources pieces of AP, or asks the same team to process more payments without adding headcount.
AI does not need to make the approval decision on its own. The better use is to create a review layer that gathers the evidence, flags unusual patterns, and gives the human approver a cleaner decision packet. Instead of asking the reviewer to open five systems and interpret several emails, automation can present the key facts in one place.
A typical vendor master data change review might examine:
- What field is changing, such as bank account, tax ID, legal name, address, remittance email, payment terms, or contact owner.
- Who requested the change and whether that person has requested similar changes before.
- Whether the supporting document matches known vendor details.
- Whether the request conflicts with open invoices, active purchase orders, or recent payment history.
- Whether the vendor is critical, high spend, new, inactive, or already under review.
- Whether the change arrived through an approved channel or through an unusual email path.
The value is not just fraud prevention. It is also consistency. A busy AP clerk may be careful but still miss that the vendor has two names in the system. A procurement manager may know the supplier relationship but not see that the request affects a scheduled payment run. A controller may approve a change during close because the amount looks small, while the vendor has a much larger payment due next week. AI can connect those signals faster than a person switching tabs under deadline pressure.
The most useful system treats vendor data changes as controlled events, not administrative errands. Each request gets captured, classified, scored, routed, and documented. The result is a healthier vendor file, fewer payment surprises, and a review process that can stand up to questions later.
Why It Matters for Businesses
Vendor master data is one of those back-office areas that quietly supports the whole company. Sales promises depend on suppliers delivering materials. Operations depends on repair partners, freight providers, contractors, and inventory vendors. Finance depends on accurate bank details, tax records, payment terms, and remittance instructions. When the master record is wrong, teams feel the pain in different places, often days or weeks after the original change.
The most obvious risk is payment fraud. A fraudulent bank update can be disguised as normal vendor maintenance. The request may include a professional-looking PDF, an email signature, and a sense of urgency. The AP team may be told that payment will be delayed unless the new details are entered today. If the approval process depends mostly on whether the attachment looks complete, the business is exposed.
But fraud is only one category. Vendor data errors also create avoidable operating drag:
- Payments fail because banking details were entered incorrectly.
- Suppliers call for updates because remittance contacts were changed without notice.
- Buyers lose time helping AP verify changes after invoices are already due.
- Duplicate vendor records distort spend reporting and weaken contract visibility.
- Tax forms do not match vendor names, addresses, or classification codes.
- Inactive vendors are reactivated without enough review.
- High-risk changes get approved with the same effort as low-risk contact edits.
These issues rarely look dramatic at first. They show up as a few bounced ACH payments, a confused supplier, a duplicate payment concern, or an audit sample that takes too long to explain. Over time, the pattern becomes a hidden cost center. The company spends more time chasing exceptions than preventing them.
For smaller and mid-sized businesses, the risk can be sharper because the same people often wear multiple hats. One AP clerk might handle invoices, vendor setup, statement reconciliation, payment runs, and supplier questions. A finance manager may review changes only when the queue is already backed up. Procurement may not have a formal vendor governance role, even though buyers know the supplier relationships best. Without a structured workflow, everyone assumes someone else checked the context.
AI and automation help by turning scattered signals into a review routine. The system can compare the request against known vendor behavior, recent activity, and required evidence before a person approves the update. It can also make the process more fair and repeatable. A bank change for a strategic supplier with an open six-figure invoice should not be treated like a phone number correction for a low-spend vendor.
This matters for audit readiness too. When someone asks why a bank account was changed, the business should not have to reconstruct the answer from inbox history. A strong workflow can preserve the request source, extracted document details, reviewer notes, approval path, risk score, and final ERP update confirmation. That record becomes useful when finance reviews controls, when auditors request samples, or when leadership wants proof that automation is reducing risk instead of just moving work faster.
The business case becomes easier to see when the team measures the right things:
- Average time from vendor change request to approved update.
- Number of requests missing required documentation on first submission.
- Percentage of bank changes requiring enhanced verification.
- Duplicate vendor records prevented or merged before use.
- Payment failures tied to vendor record errors.
- High-risk change requests stopped, corrected, or escalated.
- Hours spent by AP and procurement on manual follow-up.
These metrics give leaders a clearer conversation than generic efficiency claims. The goal is not to brag that AI touched the process. The goal is to show fewer preventable payment issues, stronger controls, faster clean approvals, and better evidence when questions arise.
There is also a customer and supplier relationship angle. A reliable vendor data process protects supplier trust. Legitimate vendors do not enjoy being asked for the same documents three times, waiting through unclear approvals, or receiving payments to old details because an update was missed. A controlled workflow can be both stricter and smoother. It can ask for the right evidence once, route the request quickly, and give the AP team a clear answer.
When vendor master data is treated casually, the business accepts invisible risk. When it is treated as a controlled workflow, finance and procurement gain a practical lever for protecting cash, compliance, and operating continuity.
The Practical Automation Opportunity
A useful AI-enabled vendor change review does not begin with a giant system replacement. It begins by defining which changes deserve which level of review. The workflow should separate routine maintenance from risky updates, then route each request with enough context for a fast, informed decision.
Start with a clear intake point. Instead of letting change requests arrive in random inboxes, route them through a form, shared mailbox, vendor portal, or ticket queue. The intake should capture the vendor name, vendor ID if known, requested change type, requester information, supporting documents, reason for the change, and desired effective date. If the request still arrives by email, automation can extract the same fields and create a structured case.
AI can help classify the request. It can read the message and attachments, identify whether the request involves banking, tax, legal name, address, payment terms, contact information, or status changes, and compare the request against policy rules. A bank account update may require callback verification and manager approval. A remittance email update may require domain comparison and vendor contact validation. A spelling correction may require lighter review.
The next step is evidence matching. The workflow can compare extracted details from the request against the vendor master record, W-9 or tax form, contract file, purchase order history, invoice history, known contact list, and recent payment activity. The system should not simply say "approved" or "rejected." It should show the reviewer what matched, what changed, and what remains unresolved.
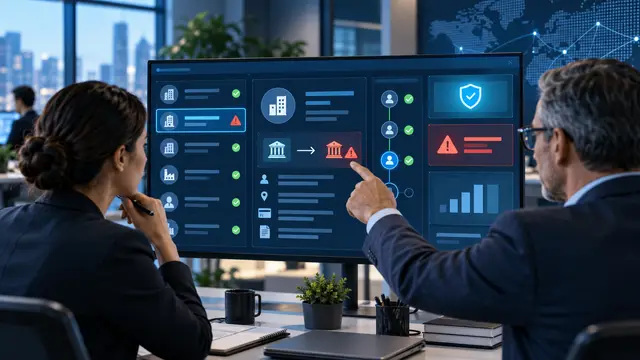
For example, imagine an AP clerk receives a request to update banking details for a packaging supplier. The vendor has open invoices worth $84,000, but the request comes from an email address that differs from the known vendor domain by one character. The bank letter has a legal name that does not match the vendor's tax record. The vendor has also not changed payment details in the last three years. A manual reviewer might catch one of those facts. An automated review packet can surface all of them before anyone changes the ERP record.
A practical review packet might include:
- Requested field changes with old value and new value side by side.
- Vendor risk profile, including spend level, criticality, and recent payment volume.
- Request source and whether the sender matches approved contacts.
- Document extraction results with confidence indicators.
- Conflicts with tax forms, contracts, invoices, or purchase orders.
- Recent vendor activity, such as last payment date and open balance.
- Required verification steps based on change type.
- Recommended routing path and escalation reason.
Human approval still matters. The point is to make the human decision better, faster, and easier to defend. The AP manager should be able to see why a request is high risk without reading every attachment from scratch. The procurement owner should be able to confirm whether the vendor relationship is legitimate. The controller should be able to review exceptions without turning every vendor edit into a meeting.
The workflow should also include a pause before ERP update. This is the control point where the business can prevent damage. Once the data is changed in the system of record, payment runs, purchase orders, vendor portals, and reporting may rely on it. Automation can hold high-risk requests in a pending state until required checks are complete. It can also prevent direct updates when the case is missing evidence.
A simple scoring model can be enough at first. The business can assign higher risk to bank changes, tax ID changes, legal name changes, new vendor activation, inactive vendor reactivation, high-spend vendors, urgent requests, unusual sender domains, mismatched documents, and changes requested close to payment dates. AI can help interpret the messy parts, such as whether a document appears to support the requested change or whether an email thread contains suspicious urgency.
The automation should produce clean audit evidence as a byproduct. Every case should preserve the original request, extracted fields, matched documents, review notes, approval timestamps, verification method, ERP update confirmation, and any rejected or revised details. This evidence should be easy to retrieve by vendor, approver, date, risk score, and change type.
Teams can roll this out in phases:
- Phase 1: Route all bank account changes through a structured intake and require documented callback verification.
- Phase 2: Add AI extraction for vendor documents and side-by-side comparison against master data.
- Phase 3: Add risk scoring based on spend, vendor status, request source, and payment timing.
- Phase 4: Connect the workflow to ERP update tasks and approval evidence storage.
- Phase 5: Review monthly metrics and tune routing rules based on real exceptions.
This phased approach keeps the project manageable. It also helps the team prove value before automating every possible vendor field. Bank changes are usually the best starting point because the risk is obvious, the volume is manageable, and the control benefit is easy to explain. After that, the company can expand to tax information, legal name changes, payment terms, duplicate vendor detection, and reactivation reviews.
Good automation should make the process easier for legitimate requests. Suppliers should receive clear instructions. AP should know exactly what evidence is missing. Procurement should only be pulled in when relationship context is needed. Finance leaders should get a short exception dashboard instead of asking for status updates across email, ERP notes, and spreadsheets.
The technology stack does not need to be exotic. Many businesses can begin with a workflow tool, an AI document extraction layer, an approval queue, and connections to ERP, vendor files, and email. The more important design choice is the operating rule: no risky vendor master data update should happen without a traceable review packet.
Business Takeaway
Vendor master data is not just a database maintenance chore. It is a payment control, a supplier relationship tool, a compliance record, and a source of truth for purchasing and finance decisions. When changes are approved with limited context, the business accepts risks that are hard to see until money, time, or trust has already been lost.
AI and automation can improve this process without taking judgment away from finance and procurement leaders. The strongest design gathers the request, classifies the change, checks supporting evidence, compares the new information against existing records, scores risk, routes the case, and preserves the approval trail. That gives human reviewers better context at the moment when their decision matters most.
The best place to start is narrow. Pick the vendor change type with the clearest risk and the most painful follow-up. For many companies, that is bank account changes. For others, it might be new vendor setup, tax profile corrections, inactive vendor reactivation, or duplicate record cleanup. Build a review workflow around that one process, then expand once the team trusts the pattern.
This week, pull ten recent vendor master data changes and ask three questions for each one: who requested it, what evidence proved it was legitimate, and where that evidence would be found six months from now.