What Happened
Vendor certificates are easy to ignore until they become the reason a job stalls, an audit
finding appears, or a customer asks for evidence the business cannot produce quickly.
Insurance certificates, safety records, security attestations, tax forms, licenses, and
quality documents often live across inboxes, supplier portals, shared drives, and
procurement systems. The expiration date is visible somewhere, but the business does not
have a reliable operating rhythm around it.
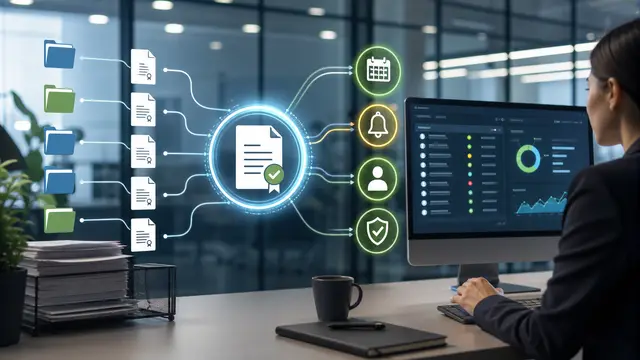
An automated vendor certificate review workflow turns those scattered documents into a
managed compliance queue. AI can read incoming certificates, identify document type, extract
effective dates, compare names with vendor records, and flag gaps. Automation can request
renewals, remind owners, escalate overdue items, and update the vendor profile. The goal is
not to create a heavy compliance program. The goal is to prevent routine evidence from
becoming an emergency.
This is a good automation candidate because the work is structured but tedious. Employees
are not adding strategic value when they rename files, scan for dates, or chase suppliers
one at a time. They add value when they decide whether a vendor can be used, whether a
missing certificate creates unacceptable risk, and whether a supplier relationship needs
attention. AI should clear the clerical fog so those decisions happen earlier.
Why It Matters for Businesses
Expired vendor documents create operational drag. A field team may be ready to schedule
subcontracted work, but procurement cannot confirm insurance. A customer may require proof
that every supplier in the chain meets specific standards. A finance team may need tax
documentation before releasing payment. When certificate status is not current, employees
improvise. They send urgent emails, approve exceptions verbally, or delay work while
everyone searches for the latest file.
The cost of that drag is measurable. Projects start late. Buyers spend time on low-value
follow-up. Managers approve risk without consistent evidence. Auditors see gaps that could
have been fixed weeks earlier. Suppliers become frustrated because requests arrive at the
last minute. A certificate workflow reduces these frictions by making renewal status visible
before the deadline matters.
For smaller and mid-sized businesses, the governance benefit can be even more important than
the time savings. A lightweight automated process creates a consistent record of what was
requested, when it was received, what changed, and who approved any exception. That record
helps the business demonstrate control without adding another manual spreadsheet. It also
reduces dependence on one employee who remembers which vendor always sends updated insurance
late.
AI improves the workflow because supplier documents are rarely standardized. One certificate
may use a different carrier name, another may list an alternate legal entity, and another
may bury the expiration date in a dense attachment. A rules-only automation struggles when
documents vary. AI can convert that variation into structured fields, confidence scores, and
review prompts, while the workflow keeps the official decision traceable.
The Practical Automation Opportunity
Begin by defining the certificate inventory. List the document types required for each
vendor category, such as general liability, workers compensation, professional license, data
security attestation, minority supplier certificate, food safety record, or quality
certification. Not every vendor needs the same evidence. A cleaning contractor, software
provider, freight carrier, and marketing consultant should not all follow one generic
checklist. Segmenting requirements makes the automation useful instead of noisy.
Next, build the intake path. Suppliers should have a dedicated upload form or email address,
and internal buyers should have a simple way to attach documents when they receive them
directly. AI can classify each attachment, extract dates, identify the named insured or
certified entity, and compare that name with the vendor master. If the match is uncertain,
the workflow should ask for review instead of silently accepting the file.
Renewal reminders should be staged. A 60-day reminder gives the supplier time to act. A
30-day reminder alerts the vendor owner. A 14-day reminder creates a visible exception. An
expiration event can change vendor status, pause new purchase orders, or require manager
approval depending on risk. The point is to make the process predictable. Suppliers learn
the rhythm, and employees stop inventing follow-up plans case by case.
The review queue should prioritize business impact. A missing certificate for an inactive
vendor is not equal to an expiring insurance document for a subcontractor scheduled next
week. The workflow can rank items using spend, open purchase orders, upcoming jobs, customer
requirements, and risk category. That ranking turns compliance from a passive file cabinet
into an operating signal.
Finally, connect reporting to action. Leaders should see upcoming expirations by owner,
vendor category, risk level, and business unit. They should also see how many documents were
accepted automatically, how many required review, and how many exceptions were approved.
This keeps the workflow from becoming a hidden administrative task. It becomes part of
procurement discipline and supplier performance management.
Create requirement profiles by vendor category instead of using one universal checklist.
Use AI extraction with confidence scoring so uncertain documents go to review.
Tie expiration priority to upcoming work, spend, and customer obligations.
Keep an audit trail of requests, submissions, approvals, and exceptions.
A practical pilot can focus on active vendors with upcoming work rather than the entire
supplier database. That keeps the first queue meaningful and avoids overwhelming employees
with low-risk cleanup. Once the process works, the same model can expand to dormant vendors,
annual review cycles, and customer-specific evidence requirements. The workflow should earn
adoption by preventing real interruptions early.
Name matching deserves special attention. Certificates often list legal entities differently
from procurement records. AI can suggest a match, but the workflow should route uncertain
matches to a human and remember the approved relationship for next time. This creates a
cleaner vendor record and reduces repeated manual review. It also prevents a certificate
from being attached to the wrong supplier simply because the names looked similar.
The renewal request should be professional and specific. Suppliers should know exactly which
document is needed, what date is missing or expired, where to upload the replacement, and
who to contact with questions. Automation should reduce friction for vendors as well as
internal teams. A clear request produces better documents, fewer follow-ups, and stronger
supplier relationships.
Business Takeaway
Vendor certificate automation is a practical way to reduce risk without slowing the
business. It gives procurement, operations, finance, and compliance the same view of
supplier readiness. The workflow does not need to be complex on day one. It needs reliable
intake, clear ownership, staged reminders, and human review where judgment matters. Once
that foundation exists, certificate status becomes a managed signal instead of a recurring
scramble.
For this specific workflow, the safest next step is a thirty day operating test with named
owners, clear thresholds, and weekly review of exceptions. The team should document every
override, every missing data field, and every case where the recommendation was useful but
incomplete. That review gives the company a grounded improvement list instead of a
theoretical automation backlog. It also keeps the implementation tied to measurable business
outcomes such as cycle time, avoided rework, reduced manual follow-up, cleaner decisions,
and better customer or vendor communication.